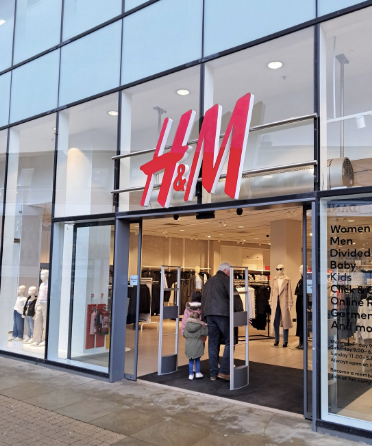
Fashion retailer H&M is investigating claims that it has been targeted by the cybercriminal group ShinyHunters. The Swedish company said it was aware of online claims relating to “a limited scope of H&M Group data”, but said it had found no evidence that its systems had been compromised. H&M confirmed it was investigating the allegations after reports that the group may have carried out an attack against the retailer.
H&M response
A spokesperson for H&M Group said the company was taking the claims seriously. They said: “We are aware of the claims circulating online regarding a potential cybersecurity incident involving a limited scope of H&M Group data. “Protecting the security of our systems and data is of utmost importance to us.” The spokesperson added that investigations were ongoing and there was currently no indication that H&M’s data environment had been breached. H&M operates around 4,000 stores across more than 80 markets worldwide. The company’s brands include COS, Weekday, & Other Stories and Arket.
No confirmed breach
At this stage, there is no confirmation that H&M has suffered a successful cyber attack. It has not been established whether hackers accessed internal systems, whether any customer, employee or supplier information was taken, or whether ShinyHunters holds genuine H&M data. There has also been no confirmation of a ransom demand or whether any external technology provider was involved. The UK’s Information Commissioner’s Office (ICO) had not received a report about the incident as of Monday lunchtime. Companies must report personal data breaches to the ICO within 72 hours of becoming aware of them if they pose a risk to people’s rights and freedoms.
Who are ShinyHunters?
ShinyHunters is a cybercriminal group previously linked to a number of high-profile data theft claims. The group has claimed responsibility for attacks involving major companies and has reportedly demanded payment in exchange for not releasing stolen information. Cybersecurity researchers have previously warned that ShinyHunters has sometimes exaggerated claims of access to victims’ systems, including presenting older or publicly available data as evidence of new breaches. The FBI has also warned that the group may claim to possess sensitive information that does not exist.
Recent cyber attacks
The investigation follows recent cyber incidents involving other major retailers. British online retailer ASOS confirmed earlier this month that attackers had obtained employee login details after impersonating a trusted contact. The company said information held on third-party platforms had been accessed, including names, contact details and some non-personal account information. Thousands of customers also received unauthorised notifications through the ASOS app. Investigators have not established a confirmed technical link between the ASOS incident and the claims involving H&M.
Security concerns continue
Cybersecurity experts say companies remain at risk from criminals using stolen credentials, social engineering and data extortion tactics. H&M said it would continue investigating the claims and would provide further information if new details were confirmed.
Originally published by UKNIP.